DevCompass
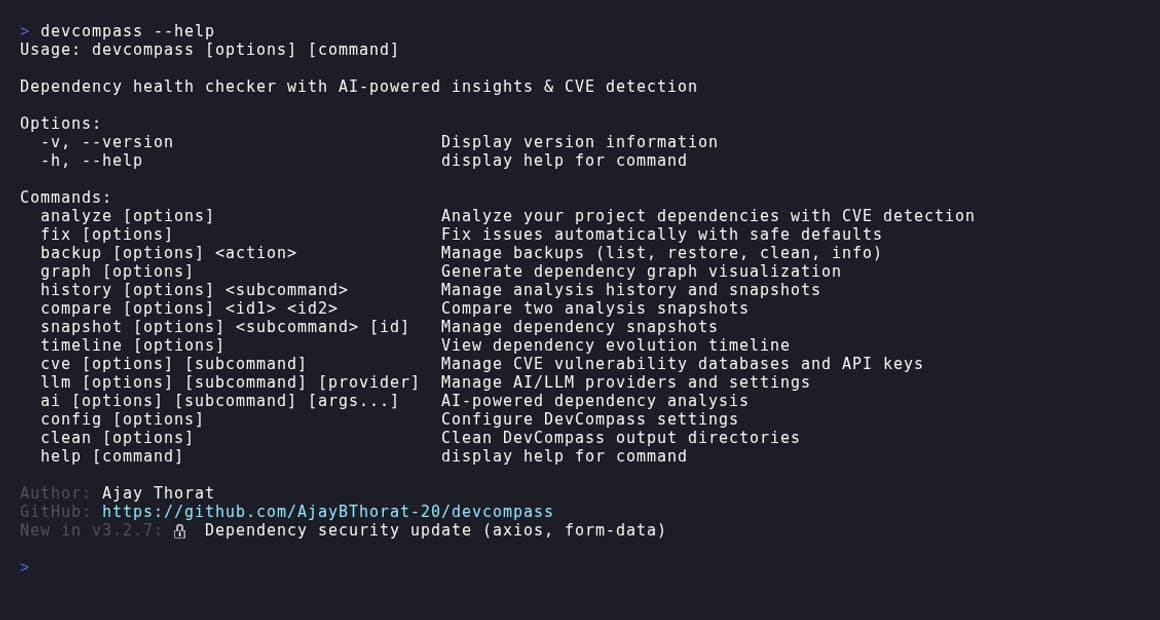
A production npm CLI I built and maintain for JavaScript dependency health. Real-time CVE scanning runs through OSV and NVD, and AI recommendations come from four LLM providers (OpenAI, Anthropic, Google Gemini, and local Ollama). The interactive D3.js dependency graph has five layouts with real-time search and filtering. Auto-fix is the riskiest part, so it ships with risk classification, dry-run previews, automatic backups, a migrate-syntax codemod engine for major-version upgrades, and a one-command undo for every fix session. Security: I fixed a shell-injection vulnerability and a path-traversal gap, moved API key encryption from unsalted SHA-256 to salted scrypt, replaced every shell-string exec with execFile and argv arrays, and closed a path where a GitHub token could follow a redirect to a third-party host. Delivery: CI runs CodeQL and OpenSSF Scorecard, enforces a 60% line-coverage floor, and blocks any release whose version is already on npm. Now at v4.1.8 with 50 published releases. Docs: devcompass.ajaythorat.com.
- Node.js
- Commander.js
- D3.js
- SQLite
- OpenAI/Anthropic/Google APIs
- GitHub Actions